
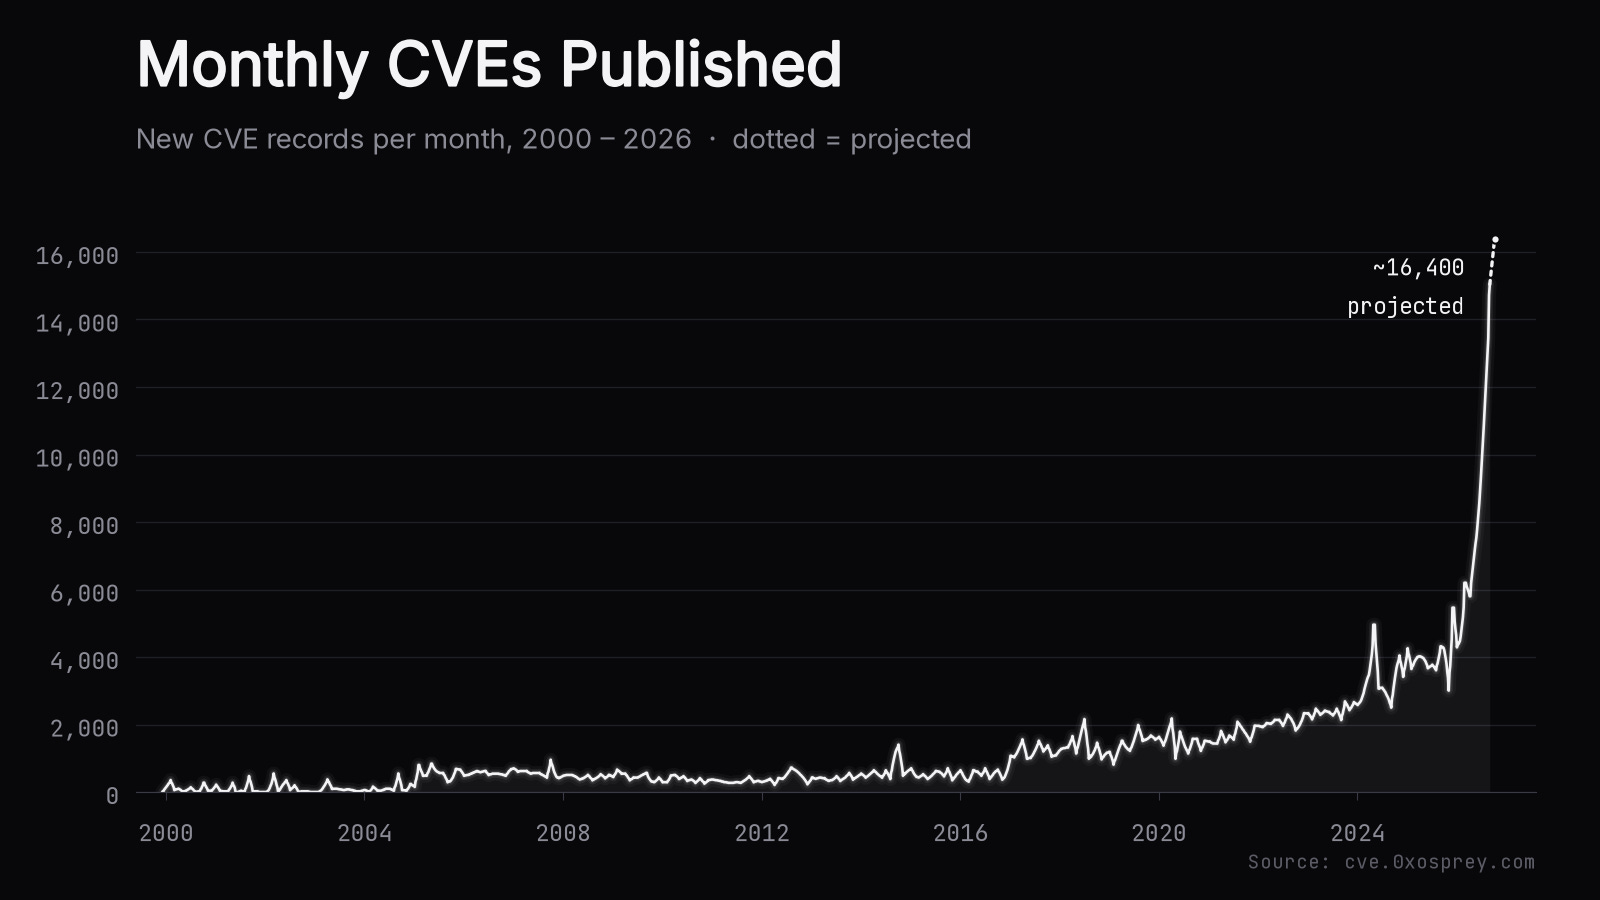
Most of you probably experienced some security-related incidents this past month, or at least saw some of the headlines. It’s being called Black October. 👻 AI is definitely a double-edged sword. It's speeding up vulnerability discovery but is also being used to quickly build new defenses and patch old code. This CVE tracker chart pretty much says it all.
Here are just a few of the crazy things that happened this month:
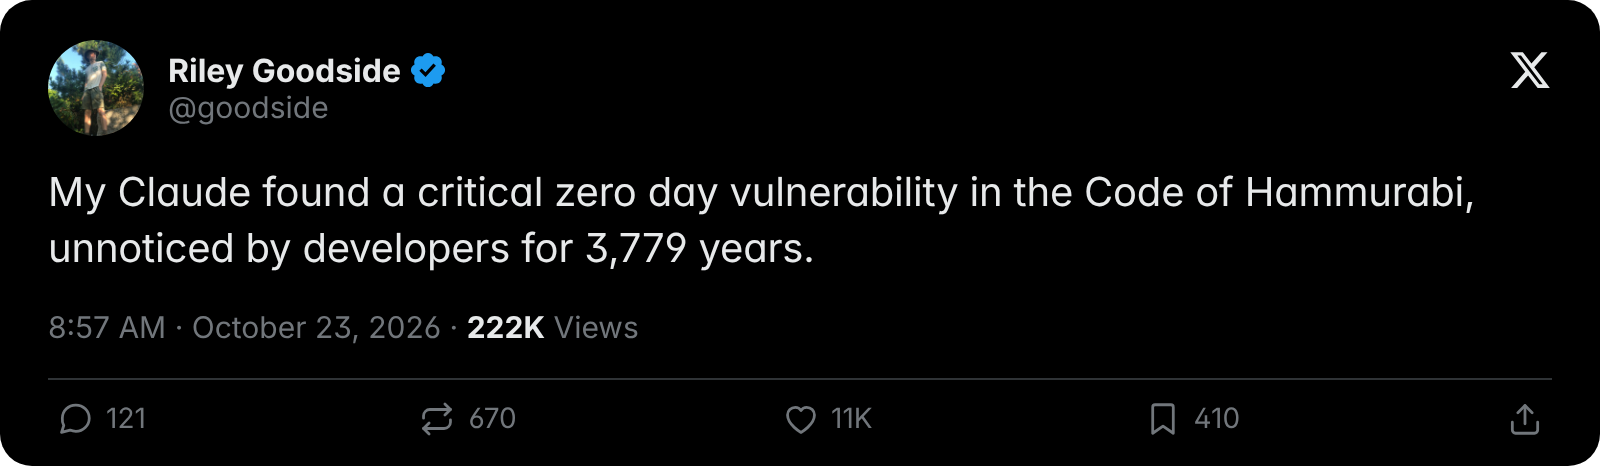
The PHP vulnerabilities (PHP2Shell) were some of the worst I’ve seen. And they actually were there for over a decade. When you have the Prime Minister of Japan posting on X about PHP, you know it’s probably not good. 😅 However, the Wordfence CEO also said they weren’t really seeing hacks.
WordPress plugins like Rank Math Pro distributing malware and TeamUpdraft exposing credentials.
WordPress core itself just patched 22 vulnerabilities with version 7.1.4. And this is the seventh core security release since July.
Compromised SSL certificates due to weak private keys. 🔑
Quest Diagnostics patient records were exposed in a security breach.
Polymarket breach due to a compromised third-party script from DebugBear RUM. FYI, if you’re using DebugBear RUM, remove their script immediately.
RCEs in GitLab, Node.js Brotli, and more.
Developer platform Railway urged all users to revoke secret keys after a cyberattack.
And those are just a few of the bigger ones. There are literally too many to list. What can you do? Honestly, it’s a good time to revisit best practices and lock down your workflows if you haven’t in a while.
If you’re using WordPress, this is honestly where using a quality managed hosting provider can really pay for itself. 💪 For example, Kinsta had all of our sites updated with the PHP patch before I even woke up. I spent a total of 5 minutes on the entire PHP fiasco. Beyond the patch, they also leveraged their Cloudflare integration at the WAF level. And it wasn’t just Kinsta; many quality hosting providers stepped up and mitigated the incident. If yours didn’t, it may be time for a change.
Take some time and update the software on all of your devices (apps, browsers, etc.), from computers and phones to robot vacuums and TVs.
Always use 2FA/passkeys/hardware keys if you aren’t already. Avoid SMS whenever someone offers one of the other options.
Utilize a password manager and services like Have I Been Pwned.
Bookmark your frequently visited sites and avoid clicking links from them in your email. It’s always better to go to the site directly.
Lock down your home network, change your Wi-Fi passwords (if you haven’t in a while), etc. 🛜
Use a VPN when necessary, especially when you’re using public networks.
Freeze your credit with the major credit bureaus. 💳
Never answer or respond to calls you think might be spam. The moment you do, you’re on their list as a target, not just probing. Use spam-blocking features from your cellphone carrier, or an app like Hiya Spam Blocker.
I’ve also wondered whether we'll plateau at some point and actually end up in a safer place? As most developers, at least I hope, are using AI to scan the security of new code they’re pushing out. But no one knows what happens next.
Updates ✍️
We pushed out an update for our Perfmatters WordPress plugin. Here are a few of the changes:
Add new perfmatters_rucss_per_id_post_types filter which allows for unique used CSS files per post ID for provided post types. 👨🔧
Adjusted Remove Unused CSS to generate separate used CSS files per taxonomy instead of one shared tax.used.css file.
Updated PHP-CSS-Parser to 9.5.0, removing the thecodingmachine/safe dependency and fixing semicolon-terminated layer statements. This improves compatibility with third-party solutions and makes parsing more reliable for anything that uses cascade layers, such as Bricks. 👍
Added a REST API exception for GenerateBlocks Pro.
Added built-in Remove Unused CSS exclusions for Elementor’s new local and global per-document stylesheets.
Updated delay JS quick exclusions for Elementor to include hooks.min.js and i18n.min.js to fix a dependency error.
Updated JS optimize script tag regex to avoid hitting PCRE backtracking limits on pages with very large inline scripts. ⚡
Added Brizy editor request parameters to the excluded page builders array.
Added logic to prevent Disable WooCommerce Scripts option from running inside page builders.
Replaced wp_admin_notice() usage in code snippets with standard admin notice markup for better compatibility with older WordPress versions.
Fixed incorrect and missing text domains, and added translators comments for placeholder strings where needed. 🌍
Fixed an issue where videos using nested source tags without a src attribute on the video element were not lazy loaded, including video tags with no attributes.
Fixed an accessibility issue with lazy video preview thumbnails where the placeholder could not be focused or activated from the keyboard and was missing a proper accessible name.
Improved picture tag lazy loading to use a more efficient source attribute migration technique and match forced attributes across the full picture markup. 🖼️
Added a sanitization callback for network settings on save.
Improved prepared SQL handling for code snippet post queries and database optimization table scans.
Security updates to improve escaping across the admin UI, including settings helpers, Script Manager, code snippets, license, support, and related screens. 🔒
Fixed a compatibility issue with WP Captcha PRO that could return a blank page when opening the Script Manager.
Fixed an issue where Delay JavaScript could skip inline scripts that contained HTML comments.
Fixed an issue where Script Manager MU Mode could save incomplete rewrite rules when WordPress rebuilt them on a request with plugins disabled, which could 404 those routes until the next full flush.
Fixed an issue where Script Manager MU Mode treated the post query argument as the current URL, so a front-end request could run another URL’s plugin rules while WordPress served the original permalink.
Fixed Script Manager MU Mode Current URL plugin rules so front page rules stay off search, feeds, and other views that share that path. The rules will also now apply correctly on private posts, pages, and the WooCommerce shop page.
Fixed a fatal error in Script Manager MU Mode when another mu-plugin read active_plugins before WordPress had finished loading.
Fixed an issue where Script Manager MU Mode could disable the wrong plugin whose folder name started with the folder of the plugin that was meant to be disabled.
Fixed a fatal error when the Login URL disabled behavior is set to the 404 template and a logged-out visitor requests customize.php before the theme has loaded. Admin requests such as wp-admin and customize.php now fall back to the disabled message, since those requests never load the front-end.
We pushed out an update for our Novashare WordPress plugin. Here are a few of the changes:
Fixed a Click to Post block editor error that could occur when certain plugins wrap block edit components via the editor.BlockEdit filter.
Fixed an issue where Pinterest share and image pin URLs did not encode the media parameter, which could break the share link when image URLs contained query strings. 📌
Fixed a PHP fatal error that could occur when one-per-line options were stored as a string instead of an array.
Added sanitization callbacks for the tools and network settings.
Hardened the settings save and import AJAX handlers. 🔒
Hardened request handling for license key saves, network settings, post meta box saves, share count refresh, and Pinterest attachment fields.
Replaced date(), parse_url(), and strip_tags() with their WordPress equivalents.
Moved block editor scripts to load in the footer. ⬇️
Improved late escaping across admin UI, settings screens, meta boxes, widgets, and frontend share markup.
We’re up for Best Performance Plugin (Perfmatters) and Content & Output Tools (Novashare) in the WP Awards. If either of our plugins has ever been helpful to you, we would greatly appreciate a vote. 🏆
We have some exciting new Perfmatters features we’ve been working on behind the scenes that are coming soon! 😁
Interesting things 🔎
Misc.
ImageFlow added a free Relight feature, and it works really well. I tried the same feature in PhotoCraft, and it wasn’t even close to the same quality.
Google Drive and Docs are getting Markdown file (.md) support. Finally!
Dan Fessler launched TrellisWM. It’s basically a window manager on steroids for macOS. Interesting idea.
Beam is also another new Mac app. Think of it like remote desktop or screen sharing, but only for the windows you want. 🪟
VMPal is probably the slickest VM software I’ve ever used! It’s lightweight, has a beautiful UI, and is built for Apple Silicon and AI agents. Windows app is also coming soon.
EA shuts down BioWare after over three decades. I never really played their games, but I have a few friends who are pretty bummed about this. The Save Mass Effect petition already has over 280,000 signatures. ✍️
The Arc browser is being sunset on December 22nd, 2026. Sridhar put together a large spreadsheet with alternatives similar to Arc.
WordPress
WooCommerce has a new default free and low-code block theme called Purple.
Speaking of new themes, my friend Alex de Borba launched Aegis. It’s a lightweight Full Site Editing (FSE) theme that combines performance with aesthetics. Check it out.
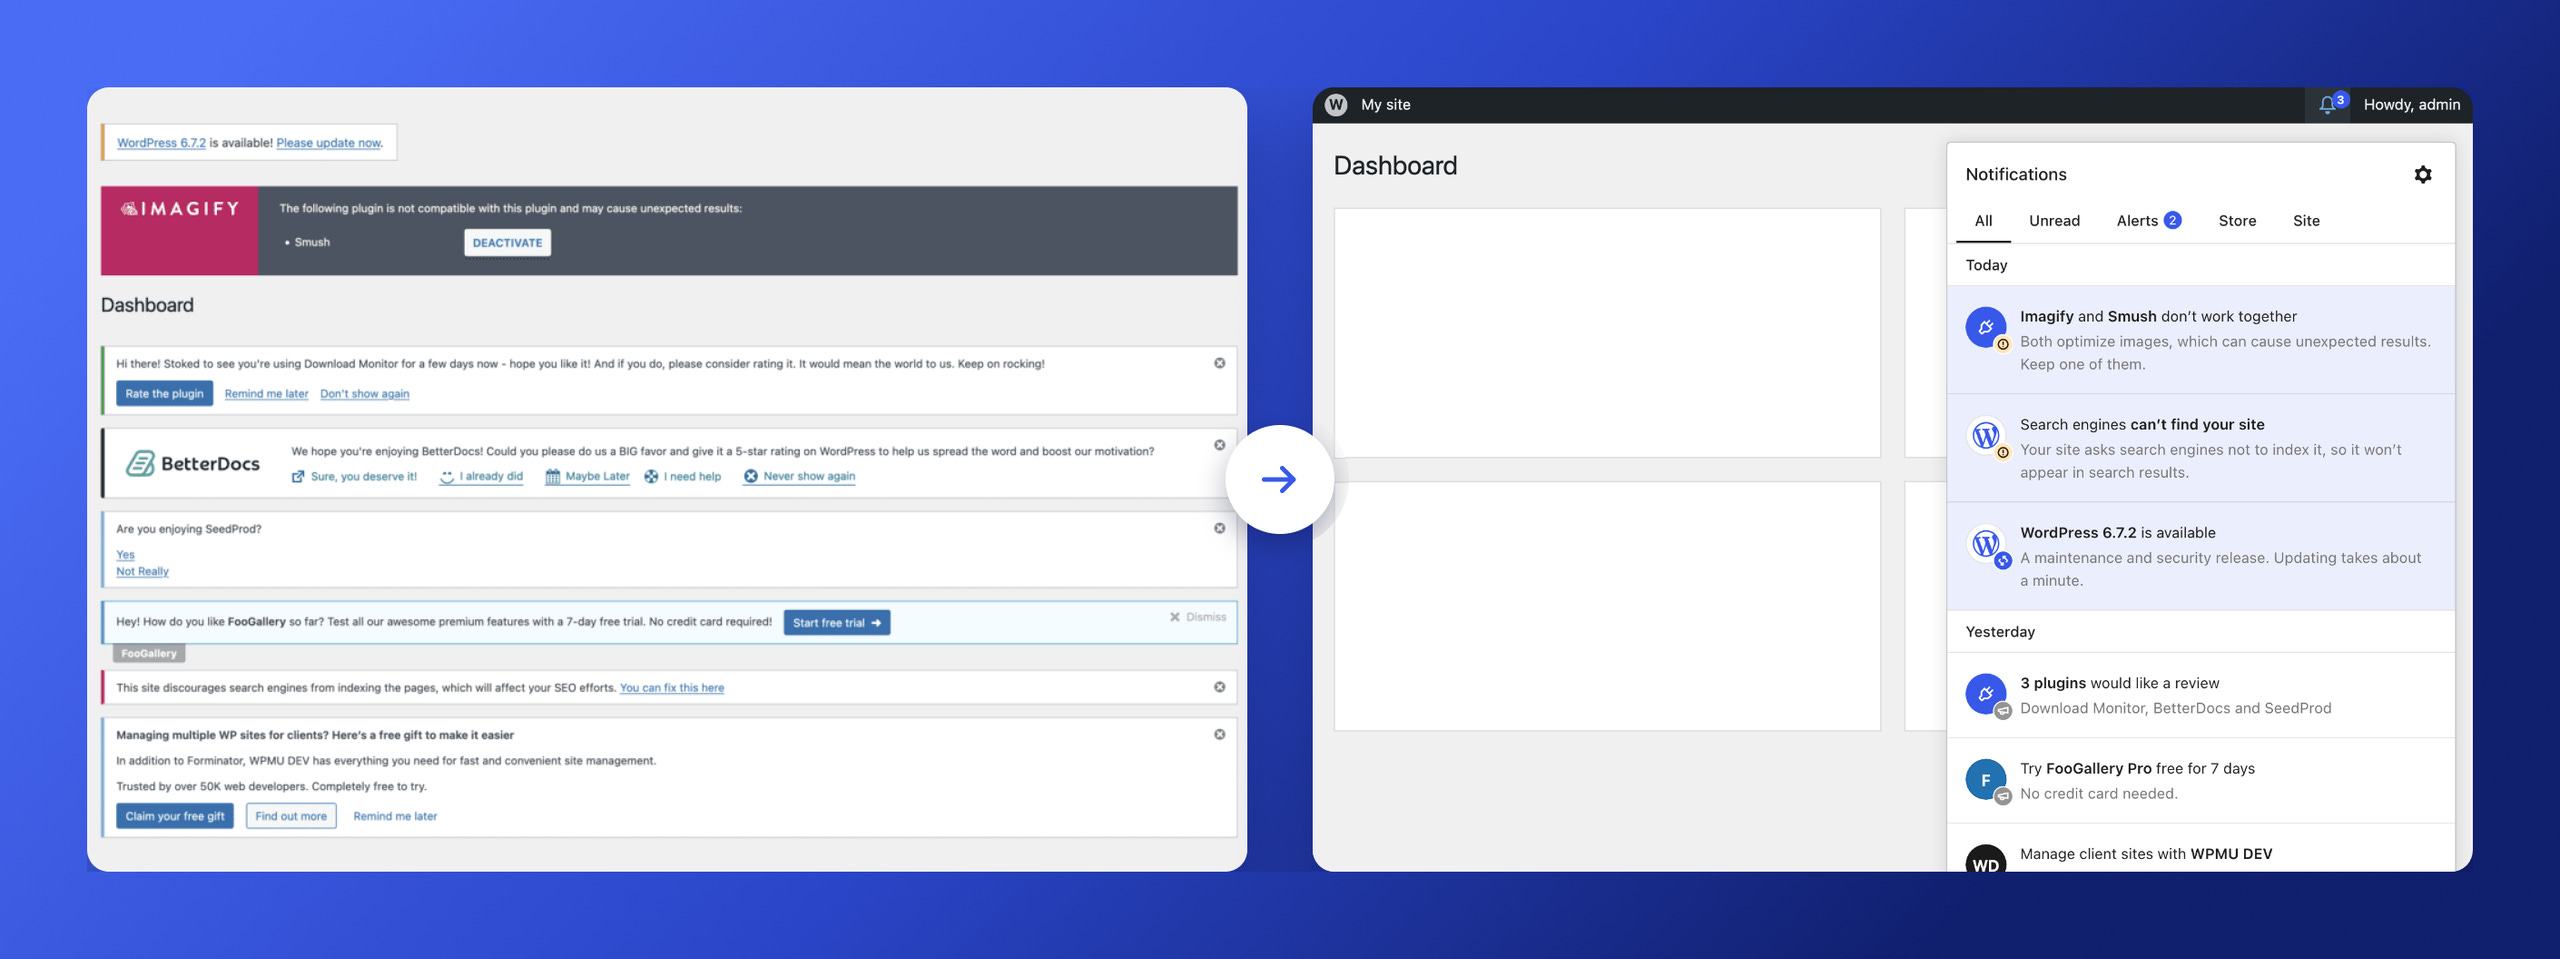
The WordPress team is working on a unified system for admin notifications that third-party plugins could also hook into. I’m all for this! No more pushing down half the screen.
Awesome Motive has taken over the popular WP Crontrol plugin. All the pro features are now available in the free version.
Did Liquid Web kill the trust that StellarWP had built? 🤔 Alex Vasquez shares his thoughts.
The WPBruiser anti-spam plugin also has a new home at WPZOOM.
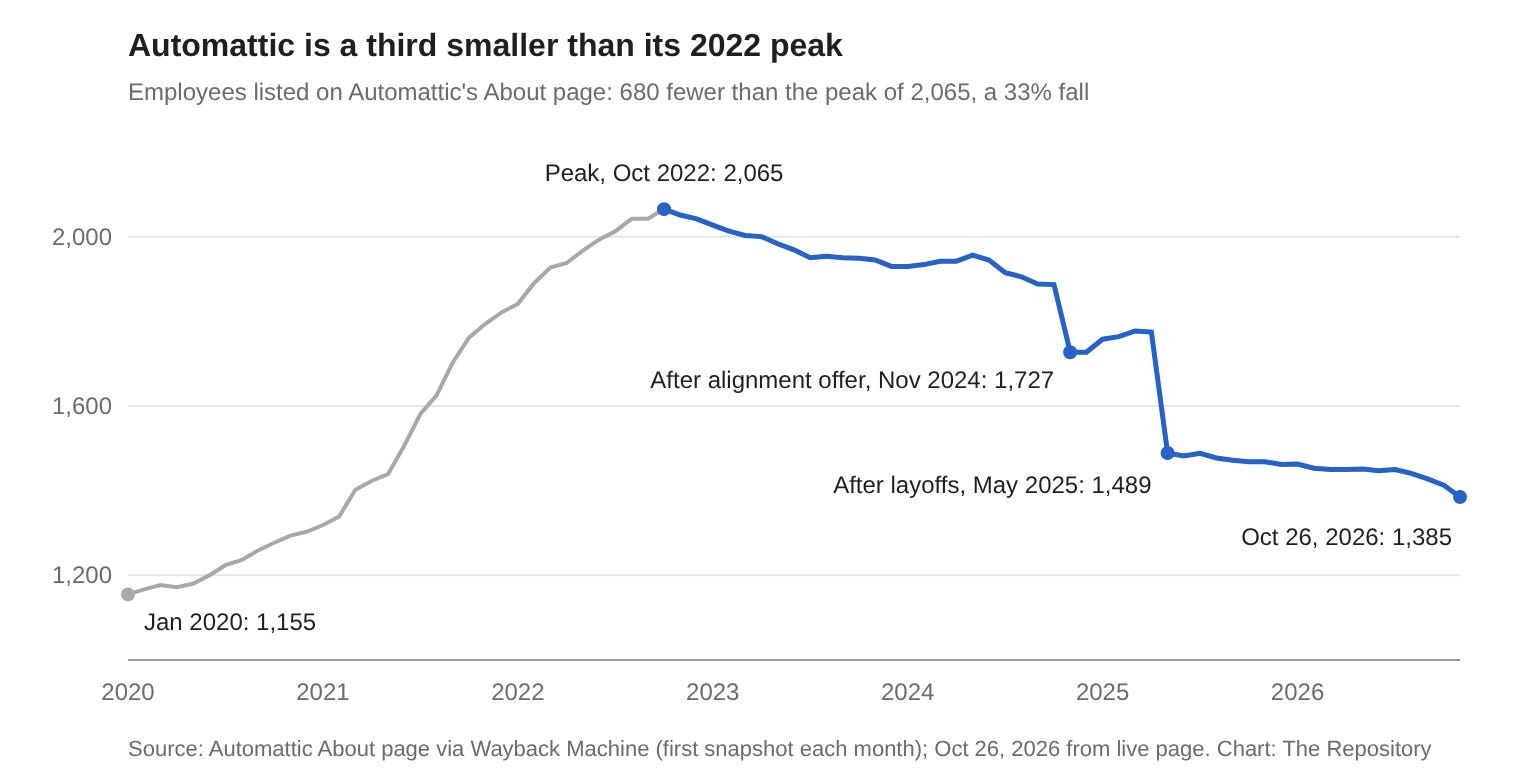
Automattic’s latest layoffs hit a workforce already a third smaller than its 2022 peak. Here’s a visualization of it.
Kinsta shipped some great new features this month!
They partnered up with Patchstack and are now including free vulnerability protection. Coincidentally, good timing for this. 🔒
You can now suspend an environment. Great for agencies and resellers who might be working with a difficult client, or perhaps waiting on payment.
There are now bulk actions in MyKinsta. For example, perhaps you want to change the PHP version on a bunch of sites at once, or enable bot protection.
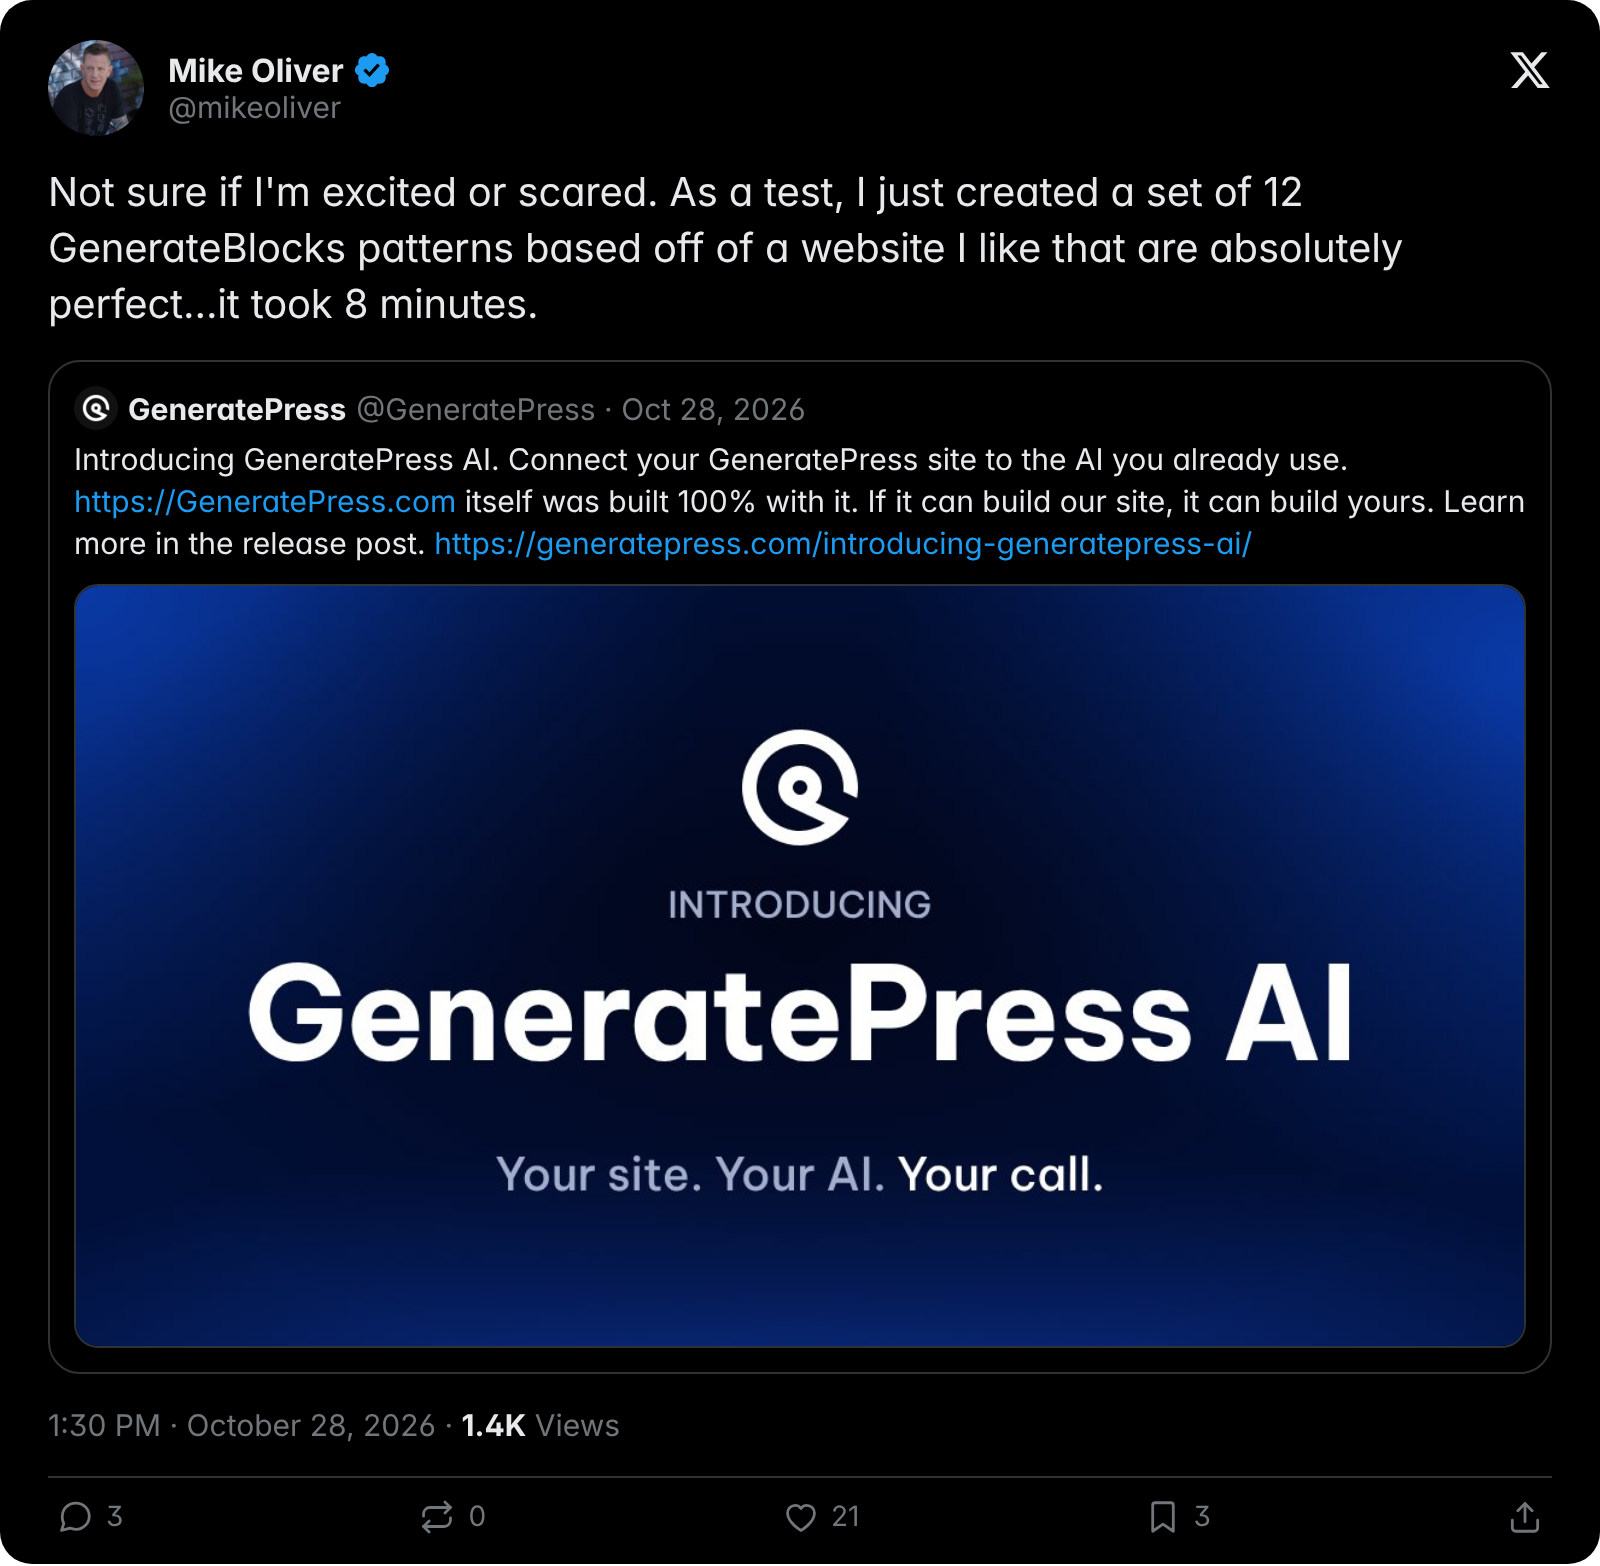
GeneratePress introduces GeneratePress AI. You install it only if you need it, meaning no AI-adjacent code is loaded in any of their core plugins. In fact, their new GeneratePress.com website was built using it. I’ll definitely be playing around with this. I also recommend checking out this short walkthrough from Kyle.
Marketing
Reddit will soon require an account for most content.
Mastodon got a complete design overhaul. 🎨
Barn2’s new sales are down 58% in two years, while renewals are up 29%. Katie dives into the five reasons behind the decline and which might be recoverable.
Google AI Overviews jump from 26% to 80% of branded queries. 😮
Bluesky wants to give you your own domain on the open web. Honestly, Bluesky handles have always been confusing, so I think this is a good idea.
Performance
Weston Ruter announced two great improvements coming to WordPress 7.2:
They are eliminating the script/style concatenation in the admin and saying goodbye to load-scripts.php & load-styles.php.
In the admin, they are also going to prefetch the blocking scripts and styles that they know will be on the next screen. ⚡
WordPress 7.2 is expanding the client-side media processing that it previously added in the editor to work in the Media Library.
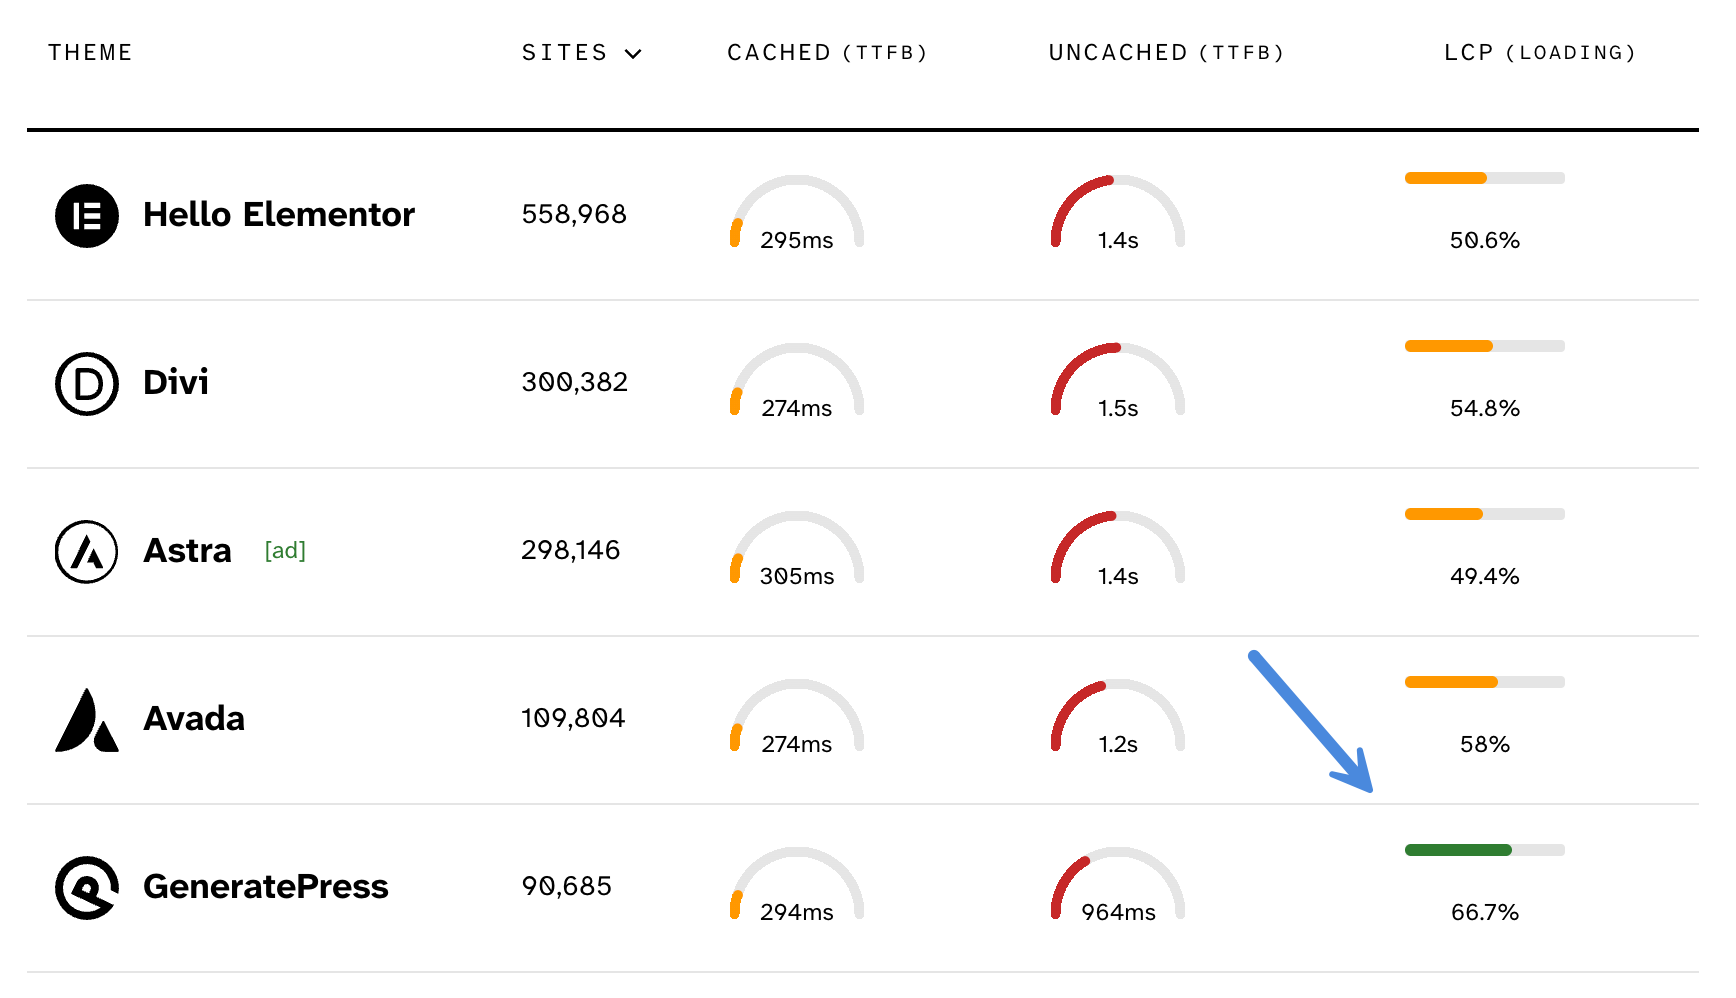
theweb.report website launched with some great WordPress and performance stats! They get most of the data by crawling domains in Google’s Chrome UX Report (so active and real websites). Love seeing how the GeneratePress theme is performing out in the wild. It’s leading in terms of good LCP %.
Query Monitor got a few nice little UI improvements. The latest version now shows the file size of enqueued scripts and styles, and the number of queries, scripts, and styles in the admin bar dropdown.
JPEG XL has now landed in all major browsers. Jake Archibald takes a look at the pros and cons in terms of performance versus WebP, AVIF, etc. 🚀
Cloudflare is about to add a feature to manage spend limits. I know many users will be happy about this.
AI
Google launched Gemini 4 Argon and Carbon, OpenAI launched GPT-6.1 Terra, Anthropic launched Claude Haiku 5.5, and Meta launched Muse Wonder. I always like to check Artificial Analysis for a broad overview of how they stack up (intelligence, speed, cost), as it’s impossible to keep up with everything.
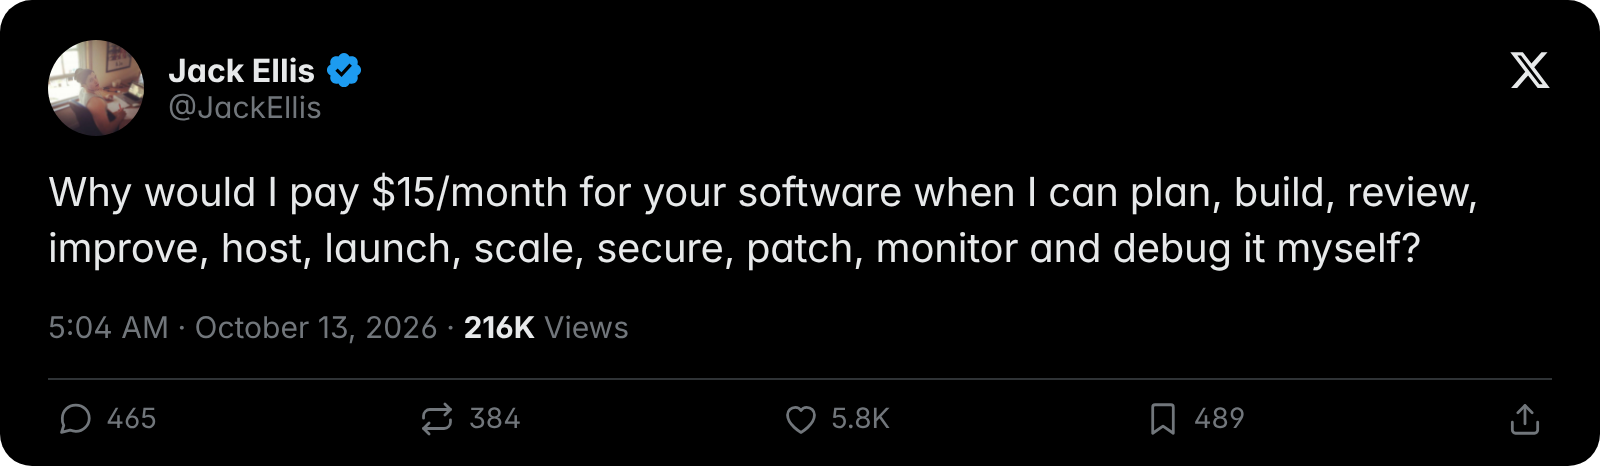
98% of US households aren't paying for AI yet.
Grok Bot may end up using the best back-end model for specific tasks, such as Claude Opus 5.5, Midjourney, or Suno.
SpaceXSI has launched a unified subscription. You can now have everything under one account for X Premium, Grok Bot, and Cursor.
Canva releases its first image generation model. 🌅
Dessa is a new conversation model from Block trained only on speech. Probably the most realistic I’ve heard so far.
If you're in the Scottsdale, AZ area, hit me up, and we can grab lunch! 🥗👋
Thank you for all you do! Your products are great and I look forward to every newsletter!